2026 Top Cloud Based Access Control What Is It and How It Works?

Time:2026-09-23 Author:Oliver
0%

As organizations prepare for 2026, security teams are asking, “what is cloud-based access control and how does it work?” The answer begins with a simple shift: access decisions move from isolated hardware to cloud-managed identity services. Instead of checking only a plastic card, the system evaluates a person, device, location, time, and requested resource. It can then approve, deny, or challenge the request with multifactor authentication.

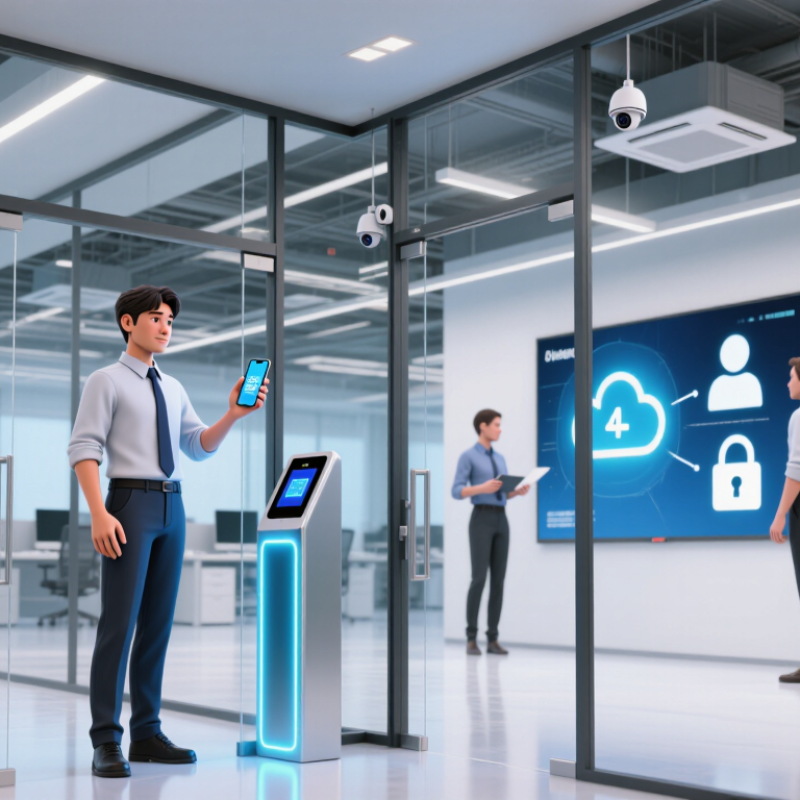
In a typical office, an employee presents a mobile credential at the entrance. The cloud platform verifies the identity through an identity provider, checks the access policy, and sends a decision to the connected lock or controller. Administrators can update permissions remotely, review entry logs, and remove access within seconds. That visibility supports least-privilege practices and clearer security oversight. It also reduces repetitive work across multiple buildings.

Bruce Schneier, a respected cybersecurity author, has said, “Security is a process, not a product.” His observation fits cloud access control well. The platform may provide useful tools, but it cannot repair weak passwords, poor onboarding, or careless permission reviews. It is not magic. Reliable results require tested policies, protected administrator accounts, regular audits, and a recovery plan for network outages. Cloud systems also introduce dependencies that some teams underestimate. A thoughtful evaluation should examine encryption, data retention, vendor support, integration options, and operational resilience. The technology is powerful, yet its effectiveness still depends on disciplined human decisions.
2026 Top Cloud Based Access Control What Is It and How It Works?

What Is Cloud-Based Access Control?

Cloud-based access control manages entry through online software, connected door controllers, and verified user credentials. Instead of storing every permission on one local computer, the system keeps access rules on protected cloud servers. An administrator can approve a worker remotely, change a schedule, or remove access within minutes. At the door, a card, mobile credential, PIN, or biometric reader sends a request to the controller. The system checks identity, time, and permission before unlocking. Each event creates a timestamped record for review.

Tips: Begin with a clear access policy. Give users only the doors they need. Enable multi-factor authentication for administrators. Review permissions every month. Test emergency power and network backup regularly. A door should not fail simply because the internet drops. Ask the installer how offline decisions are stored and synchronized later.

Security depends on more than cloud storage. Strong encryption, detailed audit logs, automatic updates, and separated administrator roles reduce avoidable risks. Experienced security teams also check door hardware, cable protection, and reader placement. A perfect system does not exist. Poor training can still expose a building, even with excellent technology. Some organizations also discover outdated staff records months later. That weakness deserves attention. Reliable operation requires testing real situations, such as a lost card, a terminated account, or a temporary visitor arriving after office hours.

Cloud-based access control manages user identities, permissions, devices, and access policies through cloud-hosted services. This approach enables centralized policy enforcement, continuous authentication, remote administration, and faster updates across distributed environments. The chart shows the share of EU enterprises using paid cloud computing services in 2023 by enterprise size, illustrating the growing environment in which cloud access controls are required.

Source: Eurostat, Digital economy and society statistics — cloud computing use by enterprise size, 2023.

How Cloud-Based Access Control Works

Cloud-based access control moves decision-making from a local panel to a secure online service. A user presents a card, mobile credential, PIN, or biometric factor at a door reader. The reader sends the credential and device status through an encrypted connection. The cloud checks identity, permissions, schedule, and door conditions before approving entry. If approved, the controller releases the lock in seconds. Fast response matters. If the network becomes unavailable, configured controllers may use cached permissions, but this feature requires careful testing.

Administrators manage doors from a browser or authorized application. They can assign access to a new employee, change schedules, or remove permissions remotely. A system log records time, location, identity, and entry result. These records support investigations and routine audits when retention settings are sensible. The system can also monitor battery levels, forced doors, and repeated failed attempts. Small details help. For example, a night alert may reveal a delivery door left open after closing.

Reliable deployment begins with an assessment of entrances, network coverage, power, and emergency procedures. Permissions should follow job duties, not convenience. Multi-factor verification can protect sensitive areas, while regular reviews remove outdated access. Clear enrollment procedures often prevent more problems than complicated features. Still, cloud access control is not magic. Poor network design, weak passwords, or incorrect schedules can create frustrating failures. A practical pilot with one entrance often exposes these gaps before a full rollout. That step is easy to skip.

2026 Top Cloud Based Access Control What Is It and How It Works? - How Cloud-Based Access Control Works
Data Dimension What It Means How It Works in a Cloud-Based Access Control System Typical Implementation Consideration
Deployment Model Access-control software and policy services are hosted in a cloud environment instead of being installed only on local servers. Administrators manage users, permissions, policies, and audit records through a secure web console or application programming interface. Common Requires dependable network connectivity and a defined offline operating policy.
Identity Source The directory or system that stores user, workforce, contractor, or service-account identities. The platform can connect to an existing directory through federation or automated provisioning, reducing duplicate account creation. Identity lifecycle ownership should be assigned clearly between the directory and the access-control platform.
Authentication The process used to verify that a person or service is the legitimate account holder. Authentication may use passwords, single sign-on, one-time codes, authenticator applications, hardware security keys, or passkeys based on WebAuthn. Use phishing-resistant methods where practical, especially for administrators and high-risk applications.
Multi-Factor Authentication Verification using at least two different factor categories, such as knowledge, possession, or inherence. A policy engine requests an additional factor when a user signs in, accesses sensitive resources, or presents an elevated risk signal. Common Factor requirements should reflect application sensitivity and user risk.
Single Sign-On One authenticated session that allows access to multiple approved applications without repeated sign-ins. The identity provider exchanges signed authentication assertions or tokens with connected applications using protocols such as SAML 2.0 or OpenID Connect. Applications must support a compatible federation protocol and correctly validate issuer, audience, signature, and token lifetime.
Authorization Model The rules that determine which authenticated identity can perform which action on which resource. Permissions may be assigned by role, group, attribute, resource ownership, device condition, location, time, or risk level. Least privilege and separation of duties help reduce excessive or conflicting permissions.
Policy Evaluation The decision process that produces an allow, deny, or additional-verification result. The system evaluates identity claims, requested resource, action, device posture, network context, and policy conditions before issuing an access decision. Policies should include a default-deny approach for protected resources and be tested before broad enforcement.
Role-Based Access Control Permissions are grouped into job or function-based roles rather than assigned individually to every user. Users receive roles through approved groups or workflows, and the role grants a predefined set of resource permissions. Common Regular role reviews are needed to prevent privilege accumulation.
Attribute-Based Access Control Access decisions use attributes such as department, data classification, device status, project, or geographic region. A policy combines attributes from the identity, resource, action, and environment to make a context-aware decision. Attribute quality and consistency are essential; inaccurate attributes can create unintended access.
Privileged Access Controls for accounts that can change security settings, manage infrastructure, or access sensitive data. Higher-risk actions can require step-up authentication, time-limited permissions, approval, session monitoring, or just-in-time elevation. Use separate administrative identities and minimize standing privileges.
User Provisioning The creation, modification, suspension, and removal of user accounts and entitlements. Provisioning can be automated through directory synchronization or the System for Cross-domain Identity Management protocol. Common Immediate deprovisioning after employment or contract changes is a key control.
Device and Context Signals Information about the device and surrounding circumstances used to assess access risk. Policies may evaluate device registration, operating-system status, encryption, network type, unusual location, sign-in time, or impossible-travel indicators. Signals should support decisions without becoming the sole security control.
Encryption in Transit Protection for data exchanged between browsers, applications, devices, and cloud services. Secure transport protocols, normally based on current versions of TLS, protect credentials, tokens, policy requests, and administrative traffic while in transit. Certificates, protocol versions, and cipher configurations should be monitored and maintained.
Audit Logging A record of authentication attempts, policy decisions, administrative changes, and access events. Events are collected centrally with timestamps, actor details, source information, target resources, and the result of the action. Protect logs from unauthorized alteration and define retention periods that meet legal and operational requirements.
Monitoring and Alerts Continuous review of access events to identify suspicious or policy-breaking activity. Rules or analytics can alert on repeated failures, unusual privilege changes, abnormal access patterns, or sign-ins from unexpected contexts. Alert thresholds should be tuned to reduce false positives while preserving investigation value.
Resilience and Availability The ability of the access-control service to continue authentication and authorization during service or network disruptions. Cloud deployments commonly use redundant service components, replicated data, health monitoring, and documented recovery procedures. Define behavior for cached sessions, disconnected devices, emergency access, and recovery testing.
Scalability The ability to support changing numbers of users, applications, devices, and access requests. Cloud infrastructure can allocate resources across distributed service components and manage policies centrally as demand changes. Capacity planning remains necessary for peak authentication loads and large policy evaluations.
Administration The methods used to configure policies, manage access reviews, and delegate security responsibilities. Web-based administration, APIs, approval workflows, and delegated administrator roles allow controlled management from different locations. Protect administrative interfaces with strong authentication, role separation, and change approval.
Access Reviews Periodic confirmation that users still need their assigned roles, groups, and permissions. Review campaigns present entitlement information to managers or resource owners for approval, removal, or escalation. Reviews should be risk-based and supported by clear ownership and completion evidence.
Main Benefits Operational and security improvements enabled by centralized, remotely managed access controls. Common benefits include faster provisioning, consistent policy enforcement, centralized visibility, easier integration, and reduced dependence on local access-control hardware. Benefits depend on accurate configuration, strong identity governance, network reliability, and ongoing monitoring.
Main Limitations Risks or operational constraints that may affect implementation and daily use. Potential challenges include internet dependency, migration complexity, integration gaps, configuration errors, subscription costs, and concentration of administrative risk. Use staged deployment, documented fallbacks, independent testing, and regular security reviews.

Core Components and Access Management Features

Cloud-based access control moves authorization from isolated hardware to a centrally managed service.

Its core components include an identity directory, policy engine, authentication layer, and audit system.

A policy engine evaluates identity, device health, location, time, and requested resource.

The directory stores users, groups, roles, and service accounts.

Authentication should combine passwords with phishing-resistant multi-factor methods.

Not enough. Keep it measurable.

NIST SP 800-207 defines zero trust around continuous verification and least-privilege access. These principles shape modern access management features.

Role-based access control assigns permissions by job function. Attribute-based rules add context, such as department or device status.

Lifecycle automation creates, changes, and removes accounts as employment status changes.

Just-in-time privileges reduce standing administrator access.

Central logs record every request, decision, and policy change.

The 2024 Data Breach Investigations Report found that compromised credentials remained a leading breach method.

That gap matters.

A reliable design also needs APIs, directory synchronization, session controls, and emergency recovery procedures.

A 2024 cloud spending forecast estimated worldwide public-cloud spending at 679 billion dollars, increasing the importance of consistent access policies across environments.

In practice, teams should test one workflow, such as a contractor entering a restricted facility from an unmanaged device.

The system should deny access, explain the reason, and alert an administrator.

Users adapt badly when decisions seem arbitrary.

No architecture stays perfect. Review permissions quarterly, measure false denials, and question unused roles before they become permanent.

Benefits, Limitations, and Security Considerations

Cloud-based access control stores permissions and activity records in a managed online platform. A door reader, mobile credential, or camera sends an access request. The platform checks identity, time, location, device status, and policy. It then allows or denies entry within seconds. Administrators can update permissions remotely, even across several facilities.

The benefits are practical. Teams can remove a departing worker’s access immediately, rather than waiting for a local administrator. Centralized logs also support investigations and compliance reviews. The 2024 Worldwide Public Cloud End-User Spending forecast estimated global cloud spending at about $679 billion, showing how widely organizations are shifting critical operations online.

However, cloud dependence creates limits. Internet outages, weak integrations, incorrect time settings, and subscription changes can interrupt access. Small configuration errors may affect every connected site.

Security needs more than passwords. NIST SP 800-207 advises treating every access request as untrusted until verified. Multi-factor authentication, least-privilege roles, encryption, and hardware-backed credentials reduce exposure. The 2024 Data Breach Investigations Report found that the human element appeared in about 68% of breaches, including mistakes and misuse.

Staff training still matters. A secure platform can be undermined by shared accounts or an unlocked administrator laptop. Offline fallback procedures are essential, yet many projects treat them as an afterthought. Test failover regularly. Logs should record who changed a rule, when, and from which device. Even then, no design is perfect.

How to Choose and Deploy a Cloud Access Control System

2026 Top Cloud Based Access Control: What Is It and How It Works?

Cloud-based access control manages doors, users, and security rules through hosted software. Administrators can update permissions from a secure web dashboard. A door reader sends an authentication request to the system. The system checks the user, schedule, device, and assigned role. It then allows or denies entry.

Choosing the right system starts with daily operational needs. List every door, user group, access schedule, and emergency requirement. Check support for mobile credentials, visitor access, multi-factor authentication, and detailed audit logs. Strong encryption, role-based administration, data backups, and clear data-retention controls are essential. Ask about uptime records and how quickly access can be restored during a network outage. Offline operation matters. Not every site has perfect connectivity.

Deployment should begin with a limited pilot. Select a few doors with different hardware and traffic patterns. Test enrollment, lost credentials, permissions, alerts, and reporting. Connect the platform to existing identity services only after reviewing security settings. Train administrators using realistic cases, such as a contractor needing access for two hours. Document wiring, network paths, and recovery procedures. Keep a manual fallback plan. It may feel unnecessary, but failures often appear during busy periods. Review the first month of access logs carefully. Unexpected entries may reveal poor role design, unclear procedures, or assumptions that seemed reasonable during installation.

FAQS

What is cloud-based access control?

It manages doors, users, schedules, and permissions through hosted online software. A reader checks a credential before the door unlocks. Each event receives a timestamp.

How does a cloud access system approve entry?

A card, phone, PIN, or biometric reader sends an access request. The system checks identity, time, device status, and assigned permissions. It then allows or denies entry within seconds.

What are the main benefits?

Administrators can change permissions remotely across several locations. They can remove a departing worker’s access quickly. Centralized logs support reviews and investigations.

What happens if the internet connection fails?

The door should keep making approved decisions through offline storage. Ask how those decisions synchronize after reconnection. Test this during a busy workday.

How can organizations improve security?

Use multi-factor authentication for administrators and separate high-level roles. Give each person only the doors they need. Protect cables, readers, and administrator devices.

What should access logs record?

Logs should show who changed a rule, when it changed, and which device made the change. Entry attempts should include time, door, and result. Review unusual entries monthly.

How should a system be selected?

List every door, user group, schedule, and emergency requirement. Check mobile credentials, visitor access, audit logs, backups, and offline operation. Uptime promises deserve careful questions.

How should deployment begin?

Start with a small pilot using doors with different hardware and traffic levels. Test lost credentials, temporary visitors, alerts, and reporting. Document wiring and recovery steps.

Can cloud access control eliminate security risks?

No system is perfect. Shared accounts, weak training, and outdated staff records can still expose a building. Technology helps, but people and procedures remain important.

Conclusion

Cloud-based access control is a modern security approach that manages entry permissions through internet-connected software rather than relying only on local hardware. This overview explains “what is cloud-based access control and how does it work” by describing how authorized users, administrators, connected locks, readers, and cloud platforms communicate to verify identities and control access in real time. It also introduces important features such as role-based permissions, remote administration, activity records, temporary credentials, alerts, and integration with other security systems.

The article also examines the main benefits, including flexible management, easier system expansion, centralized monitoring, and reduced on-site maintenance. At the same time, it discusses limitations and security considerations, such as internet dependence, account protection, data privacy, system availability, and backup procedures. Finally, it provides practical guidance for choosing and deploying a suitable solution by considering organizational needs, installation requirements, user capacity, access policies, security controls, support services, and long-term operating costs.
Oliver

Oliver

Oliver is a seasoned marketing professional with a wealth of expertise in driving brand awareness and engagement. With a deep understanding of our company's product offerings, he consistently delivers high-quality content that enriches our professional blog. His insights not only shed light on......